

Two-factor page
TOTP verification with six OTP slots, device trust checkbox, backup code link, and human recovery promise.
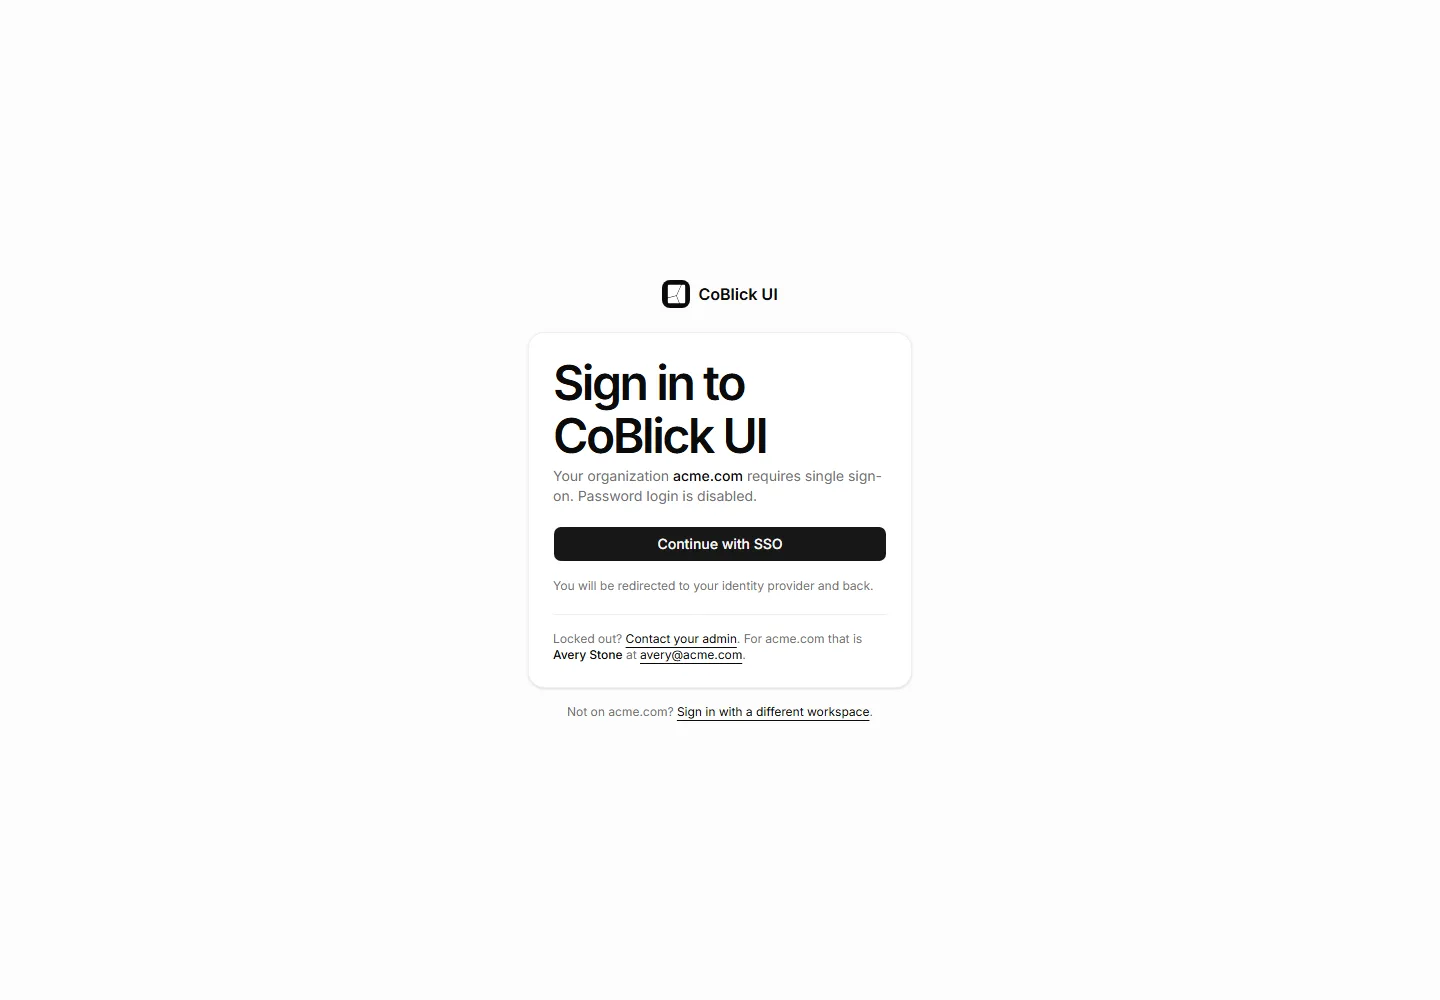
SSO-enforced sign in card with org domain shown, a single Continue with SSO button, and a named admin fallback for lockouts.
TOTP verification with six OTP slots, device trust checkbox, backup code link, and human recovery promise.
Check-your-inbox state showing the sent address, a throttled resend button, a change-email link, and the 24-hour expiry note.
Returning user login showing the known account avatar and email with a single password field, passkey option, and a use a different account escape hatch.
Post sign in workspace chooser listing memberships with marks, member counts, and role badges, plus a create workspace action and sign out link.
The invite named, inviter, role, what it grants, and the days left to accept.
An account collision gate showing a Google sign in beside an existing password account, a link action, and a password sign in fallback.
Account recovery card with an email lookup form and three recovery options listed by speed, plus a plain explanation of why identity review takes up to 3 days.
A workspace join waiting state with a step timeline, the named admins who decide, the typical response time, and a withdraw request action.
Recovery code save step with an eight code grid, download and copy actions, a saved confirmation checkbox, and a one time use warning.
Account deactivation state page naming who deactivated the account and when, listing what reactivation restores, and linking directly to the named admin for recovery.
New device verification gate showing device, location, time, and account with approve and deny actions and an honest account-lock security note.
Email change confirmation page showing the new and old address with timestamp and device, a lock account alarm for unauthorized changes, and a dual address notice.


